Loading...


Hosted Fields provide the most flexibility to the checkout experience while still adhering to the minimum PCI DSS requirements. Hosted Fields are prebuilt but customizable fields that accept customer card data, from which a single-use token is created to use as payment instead of the sensitive data. The token can then be stored so that the non-sensitive data can be reused, making future purchases easier for your customers.
Hosted Fields are ideal for capturing card details at any point in the checkout process, driving a customer flow that is unique to your needs. For example, you can accept an email address, billing and shipping details, a discount code, or whatever custom information you require from your customer. When it comes to customization, you’re really only limited to the token’s expiration setting and whatever you can capture within that time frame.
For merchants, the benefits of Hosted Fields include:
Here's an example of a fictitious company's checkout page using our prebuilt payment fields.
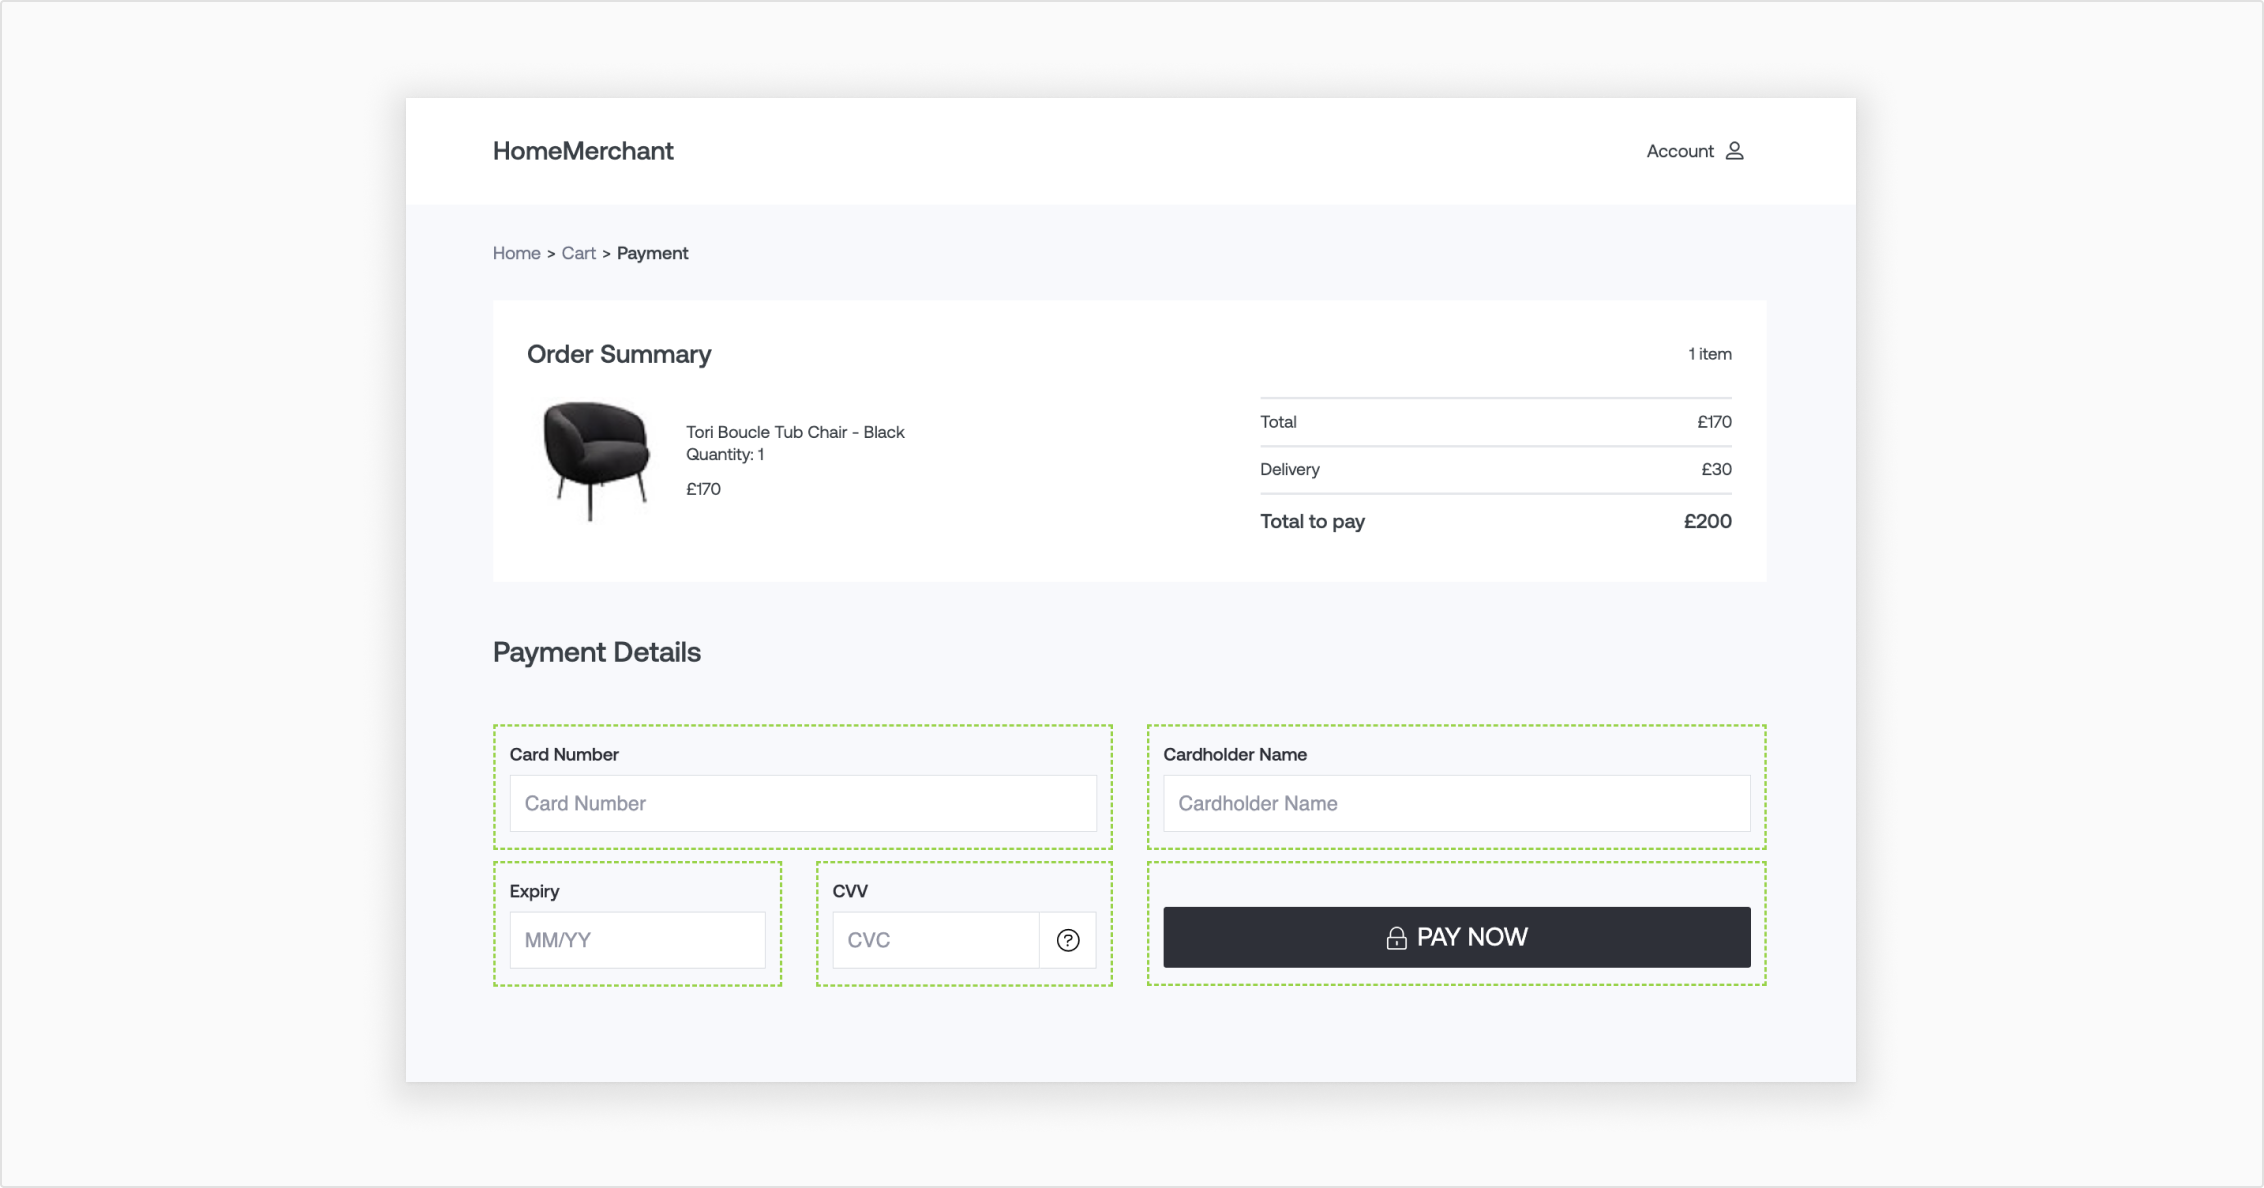
In this section, we present some “real world” examples that can be enabled through our Hosted Fields solution. Keep in mind that this section doesn’t cover all of the use cases.
A large corporation wants to ensure that they are processing their transactions in a secure environment that is also PCI DSS compliant. Integrating with Hosted Fields means that sensitive card information is captured directly by us instead of their own website.
A well-known airline wants the ability to customize the payment form to match the UI of their site to keep it familiar to the customer. Integrating with Hosted Fields means that the airline will have full control over the styling and placement of the individual fields in the payment form.
A large online store wants to improve the efficiency of their customer support. With Hosted Fields, requests and responses are shared between the merchant and us. Most of these logs are available to support members, meaning that issues can be identified and investigated accordingly between the two parties.
When a customer submits the payment form, we create a single-use, or time-limited, token to represent the sensitive data (it expires after 30 minutes). This token can then be used in requests to take payments and authenticate via 3D Secure. Once converted to multiple-use, the token can store non-sensitive card data (that is, no security code) and any additional customer details for subsequent purchases.
This single-use token is different from an access token, which we require for all requests and has a configurable expiration limit. A new access token with the required permissions must be created when performing a payment request or authentication.
At a high level, Hosted Fields work like this:

Hosted Fields Typical Flow
To try Hosted Fields, follow the steps and code samples in our guide.
Remember to first register for a developer account if you don't already have one. Once logged in, you can request Sandbox credentials from your account.